Practical AI governance,
built for organizations that need to run it.
AISGRC helps leaders turn AI governance expectations into clear ownership, usable controls, and an operating model their teams can sustain. It is a founder-led practice delivered by a small senior team of governance, risk, privacy, and security specialists.
AISGRC is built on 20 years of governance and risk-management leadership in the financial sector, and on The AI Governance Practitioner's 90-Day Playbook, the methodology behind the Premium Toolkit and the 90-Day Implementation Sprint.
The approach is informed by ISO/IEC 42001, NIST AI RMF, the EU AI Act, and applicable guidance. The objective is not to add another framework. It is to turn those expectations into an operating model that fits the organization.
The standards describe the destination.
AISGRC provides the practical route.
ISO/IEC 42001, NIST AI RMF, the EU AI Act, and applicable guidance each describe what good AI governance looks like. None of them tell an organization how to operationalize it. AISGRC closes that gap with decisions, artifacts, ownership, and a sequenced implementation path.
One operating model, organized across
18 governance domains and five operating layers.
#Governance18 synthesizes the major global standards into a structure your board can follow, your legal team can defend, and your operators can run without constant escalation. The taxonomy matters because it turns scattered obligations into one accountable model.
- 01
Assess
Establish where the organization stands across the 18 governance domains.
- 02
Prioritize
Sequence the work: what to establish first, who owns it, and why it matters.
- 03
Build
Put the operating model into practice with artifacts, decision rights, and reporting.
Certified in AI governance (AIGP), information security (CISSP), and data privacy (CDPSE).
Twenty years of governance -
long before AI made it urgent.
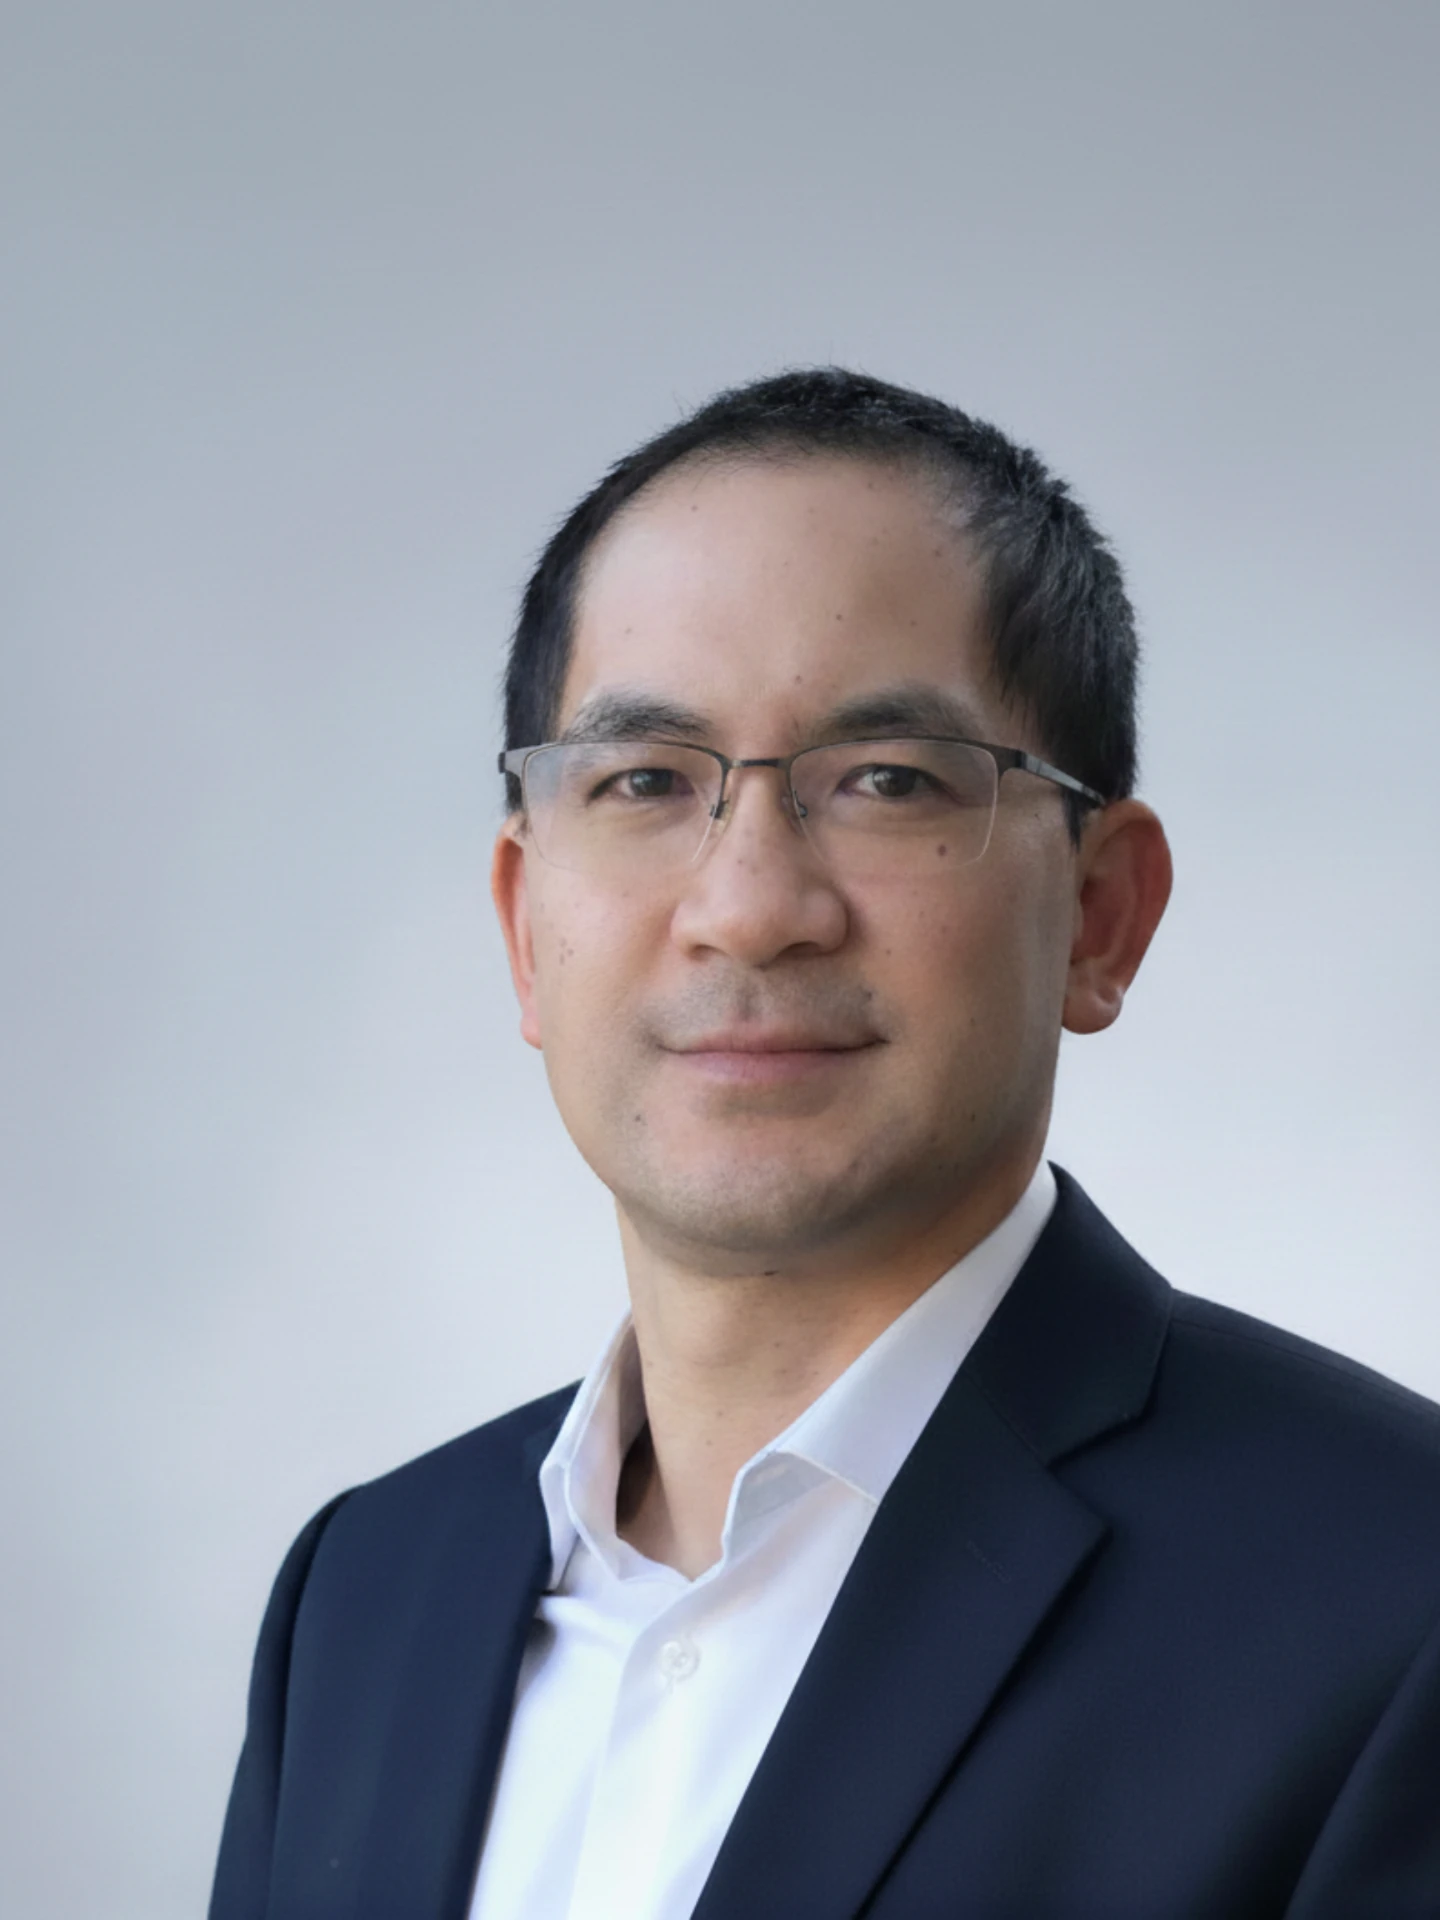
Dennis spent two decades inside financial services and at the Bank of Canada designing strategy, governance programs, and risk frameworks that had to hold up under regulator scrutiny. He represented Canada in international cybersecurity forums and has mentored the next generation of risk and security professionals throughout his career.
He holds a Master of Science in Information Assurance. His hands-on work spans assessing critical infrastructure systems, building multi-million-dollar security programs, and implementing the NIST Cybersecurity Framework and NIST SP 800-53 controls. He has been applying AI models to security problems since 2018, with a peer network across North America, Europe, and Australia.
Dennis Ah-King leads every engagement, working with a small senior team of governance, risk, privacy, and security specialists who prepare, analyze, tailor artifacts, and quality-check every deliverable.
Dennis stays accountable for every engagement end to end. The team gives that work depth and continuity - so clients get a named lead and specialist coverage, not a rotating bench.
AISGRC distills that work into an operating model leadership teams can actually run - pragmatic first, defensible second, and never academic.
A founder-led practice, delivered by a small senior team.
Dennis Ah-King leads every engagement, working with a small senior team of governance, risk, privacy, and security specialists who prepare, analyze, tailor artifacts, and quality-check every deliverable.
Governance & risk
Operating models, decision rights, risk registers, and board-ready reporting.
Privacy & data protection
Data handling, cross-border exposure, and privacy obligations mapped to your AI use.
Security & assurance
Controls, third-party and vendor review, incident response, and evidence quality.
AI/ML advisory
Model, tooling, and deployment context so controls fit how your systems actually work.
- Mid-market and growth-stage organizations scaling AI that need a defensible operating position
- Risk, security, legal, or executive leaders owning the AI question
- Teams that need to turn a stalled or fragmented governance effort into a sequenced build plan
- Organizations that need a defensible foundation and clear next steps - not an extended strategy exercise
- You are seeking academic framework summaries rather than a practical implementation system
- You want to outsource decisions instead of make them
- You need legal counsel or formal regulatory representation
- You expect a permanent external retainer
Practitioner-built.
Not partner-pitched.
Many governance engagements begin with a long discovery phase and hand implementation to a different team. AISGRC works differently: the team that designed the model, led by its founder, works directly with your team to establish a clear governance foundation, then build and hand over the operating model.
The Sprint establishes your governance foundation in the first 30 days, then builds, tests, and hands over the operating model across the following 60 days.
See the 90-Day Sprint phases →“Dennis's experience gives him insight into the real challenges organizations face - not just theoretical ones. His honesty about governance being a journey, and the human side of it, is rare and refreshing.”
Explore the 18 governance domains.
A practical article series showing how each domain contributes to an AI governance operating model your team can run.