Build an AI governance program
your organization can actually run.
Turn AI activity into clear ownership, proportionate controls, and defensible decisions - without assembling a program from scratch.
Aligned with ISO/IEC 42001, NIST AI RMF, the EU AI Act, and leading global guidance.
When ownership and controls are unclear, AI risk compounds while decisions slow down.
Free 2-minute assessment. 8 questions, a scored gap profile, and your top three priorities - shown on screen and sent to the email you provide.
Built for organizations ready to own their AI governance.
For organizations with 50–2,000 employees already using or scaling AI - and the risk, security, legal, and executive leaders accountable for governing it.
- Mid-market and growth-stage organizations scaling AI that need a defensible operating position.
- Risk, security, legal, compliance, or executive leaders accountable for governing AI.
- Teams that need to turn a stalled or fragmented governance effort into a sequenced build plan.
- Organizations that need a defensible foundation and clear next steps - not an extended strategy exercise.
- Organizations seeking academic framework summaries rather than a practical implementation system.
- Buyers who want to outsource decisions instead of make them.
- Engagements that need legal counsel or formal regulatory representation.
- Teams expecting a permanent external retainer.
Not sure which path fits? Take the 2-minute Scorecard →
Knowing the frameworks is not the same as running an AI governance program.
Most organizations know they need policies, oversight, accountability, and vendor controls. The hard part is deciding what to establish first, who owns each decision, and how to turn the work into day-to-day practice.
- Executives ask who owns AI risk - and no one has a clean answer.
- Technical, legal, risk, and business teams make decisions from different assumptions.
- The program stalls because the next practical step is unclear.
- Undocumented decisions and unmanaged exposure accumulate over time.
The board asks who owns AI risk. No one has a clean answer. That moment is exactly what this program was built for.
From uncertainty to a working program in three steps.
Assess. Prioritize. Build. The same three steps run through every offering.
- 01
Assess your current position
Use the Scorecard or a structured assessment to identify governance gaps across the areas that matter most.
- 02
Prioritize the work
Receive a sequenced roadmap that identifies what to establish first, who owns it, and why it matters.
- 03
Build the operating model
Use implementation-ready artifacts, or implement with AISGRC over 90 days to build, test, and hand over the operating model.
The tools your team needs to govern AI in practice.
Each artifact connects to a wider operating model, so decisions, accountability, and controls work together. Six of the most-used deliverables are below.
Maturity Assessment
See exactly where you stand across all 18 domains and what to address first.
Strategic Roadmap
Turn the gaps into a sequenced program your team can actually run.
AI Council Charter
Create a decision forum with clear authority, membership, and escalation paths.
Governance RACI Matrix
Make ownership unambiguous for every governance function and decision.
AI Incident Response Plan
Detect, contain, and resume operations after an AI-related incident.
Board Intelligence Tool
Give the board a defensible view of AI risk before it is asked for.
Artifacts in the full library
Governance domains covered
Standards mapped: ISO 42001, NIST AI RMF, EU AI Act, OSFI E-23
See what you get.
A quick preview of the templates and tools included in the Premium Toolkit.
AI Governance Suite Showcase
Walk through some of the templates and tools included.
Open the toolkit showcase →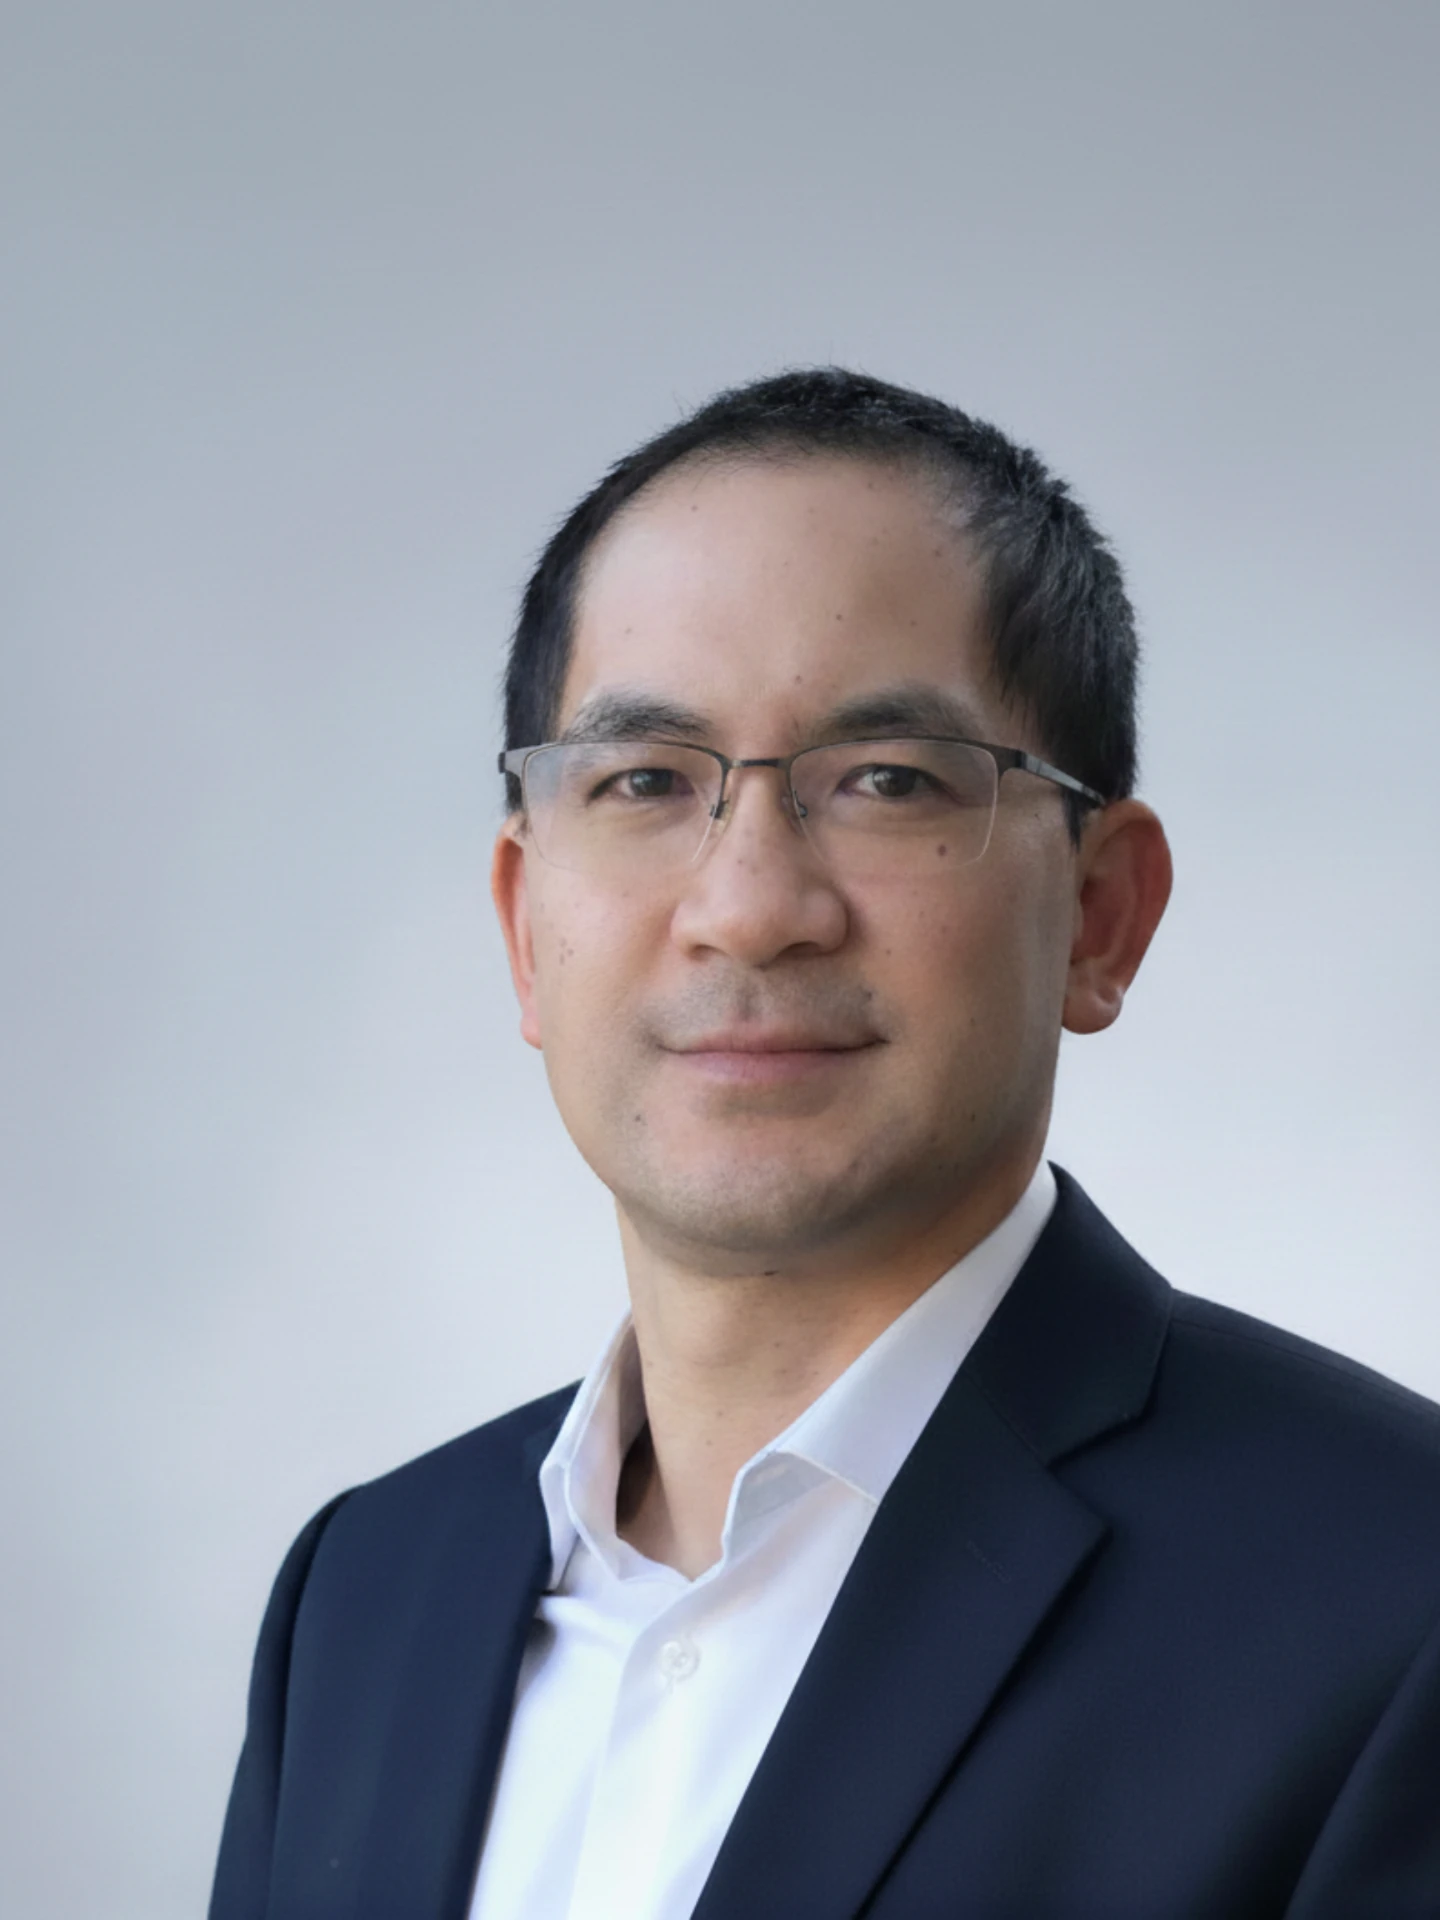
20+ years translating frameworks into practical governance.
Built by a former Bank of Canada security risk and governance leader with 20+ years in regulated, complex environments - across strategy, governance, and risk in financial services.
Dennis Ah-King leads every engagement, working with a small senior team of governance, risk, privacy, and security specialists who prepare, analyze, tailor artifacts, and quality-check every deliverable.
Pick the level of support
your organization needs now.
Start free with the Scorecard, build it yourself with the Premium Toolkit, or have it implemented with you in the 90-Day Sprint. Every path ships practical artifacts your team can use immediately.
The Scorecard
An 8-question browser diagnostic that scores your posture and names your top three priorities.
For leaders who need a quick, evidence-based starting point before choosing a path.
Premium Toolkit
39 consulting-grade artifacts, a guided diagnostic, and a sequenced 90-day build plan.
For capable internal teams that need structure, artifacts, and a sequenced build plan.
90-Day Sprint
Hands-on implementation of a working AI governance operating model in three phases over 90 days.
For organizations that need led implementation, a working model, and ownership transfer in 90 days.
No retainer.Clear scope.Practical deliverables.
- Bank of CanadaTwo decades in financial-services governance and risk, including the Bank of Canada
- AIGP · CISSP · CDPSECertified in AI governance, information security, and data privacy engineering
- International forumsRepresented Canada in international cybersecurity forums
“Dennis's experience gives him insight into the real challenges organizations face - not just theoretical ones. His honesty about governance being a journey, and the human side of it, is rare and refreshing.”
Choose your starting point.
Start with the Scorecard if you need to understand your current position.
Take the free Scorecard →Choose the Premium Toolkit if you have an internal owner and want to build with a proven sequence and ready-to-use artifacts.
View Premium Toolkit details →Choose the 90-Day Sprint if you need senior guidance and a working operating model implemented with your team.
View 90-Day Sprint details →
No retainer.Clear scope.Practical deliverables.